



|
In the present day, we’re saying the overall availability of AWS Continuum for code vulnerabilities. AWS Continuum is a safety service that finds and validates code vulnerabilities, then delivers fixes as patches you may automate or as pull requests in your repositories. AWS Continuum for code vulnerabilities confirms which findings are exploitable in your setting, ranks the ensuing points by enterprise affect, and proposes a repair for every one. Each remediation begins in a mode the place Continuum proposes the repair and an individual approves it earlier than it ships. Sooner or later, it is possible for you to to resolve which actions Continuum can take by itself, throughout the guardrails you outline.
Utilizing frontier synthetic intelligence (AI) fashions, menace actors can flip a vulnerability disclosure into working exploit code in minutes, and the identical instruments that velocity up growth additionally improve the amount of findings your groups should course of. In case your group runs a big utility property, your scanners doubtless produce hundreds of findings a day, and plenty of of them want no motion. A discovering will be unreachable, unexploitable, or already mitigated by a runtime management. Generic severity scores don’t let you know which assets a menace actor can really attain, so a vital rating on a dev-only utility appears the identical as a medium rating on a service one step away from a funds database. Beforehand, confirming whether or not a discovering was exploitable took hours of guide investigation, and delivery a repair with confidence took days of coordination throughout safety, infrastructure, and utility groups, as a result of the blast radius of a change is difficult to evaluate with out enterprise context. To shut that hole, Continuum proves which findings are exploitable and bounds the danger of every repair it proposes.
Continuum builds a context graph from two main sources: your code repositories and your AWS setting. For AWS, you arrange a collector within the account and Area the place your code runs. The collector gathers useful resource particulars reminiscent of AWS Config assets and community configuration so Continuum can choose whether or not a vulnerability is reachable over the community and what a menace actor may attain from it. From this graph, Continuum learns which programs are business-critical, who owns them, how companies rely upon each other, and which knowledge every one touches. It makes use of that image to establish your highest-value programs, reminiscent of buyer knowledge shops, cost pipelines, and authentication companies, after which ranks every ensuing difficulty by how shut its assault path runs to these programs.
Continuum analyzes every discovering towards your code and its setting context and assigns an proof stage, reminiscent of a verdict confirmed by static evaluation of the weak code path. For findings it could possibly reproduce, Continuum runs the exploit in an remoted sandbox and attaches proof-of-concept code with the replica steps. It produces the assault path, the supporting supply evaluation, and a blast radius evaluation as a substitute of a threat rating alone. It additionally evaluates whether or not your current defenses would detect and cease the validated path.
For every confirmed difficulty, Continuum generates a repair (a code patch, a dependency improve, or a configuration change) and opens it as a pull request in your related repository, able to evaluate. Each repair requires human approval: you evaluate and merge the pull request, so the ultimate determination stays together with your staff. Sooner or later, it is possible for you to to construct confidence in particular remediation lessons and let Continuum apply these fixes mechanically as soon as its confidence gates move, reminiscent of take a look at protection, scope bounds, and historic success fee.
AWS Continuum for code vulnerabilities in motion
To point out how this works, I open AWS Continuum within the console and go to Code vulnerabilities. Earlier than I can evaluate points, I arrange an setting. I join a code supply, both a GitHub integration or an Amazon S3 bucket, after which create an setting that scans it on a schedule I select. An Amazon S3 supply has a few conditions: the bucket sits in the identical account and AWS Area the place I activate AWS Continuum, and I grant entry by way of an AWS Id and Entry Administration (IAM) function that AWS Continuum assumes. I can optionally add AWS infrastructure context by establishing an AWS Continuum collector within the account and Area the place my code runs and authorizing my setting to make use of it. For the total necessities and steps, see the AWS Continuum Person Information.
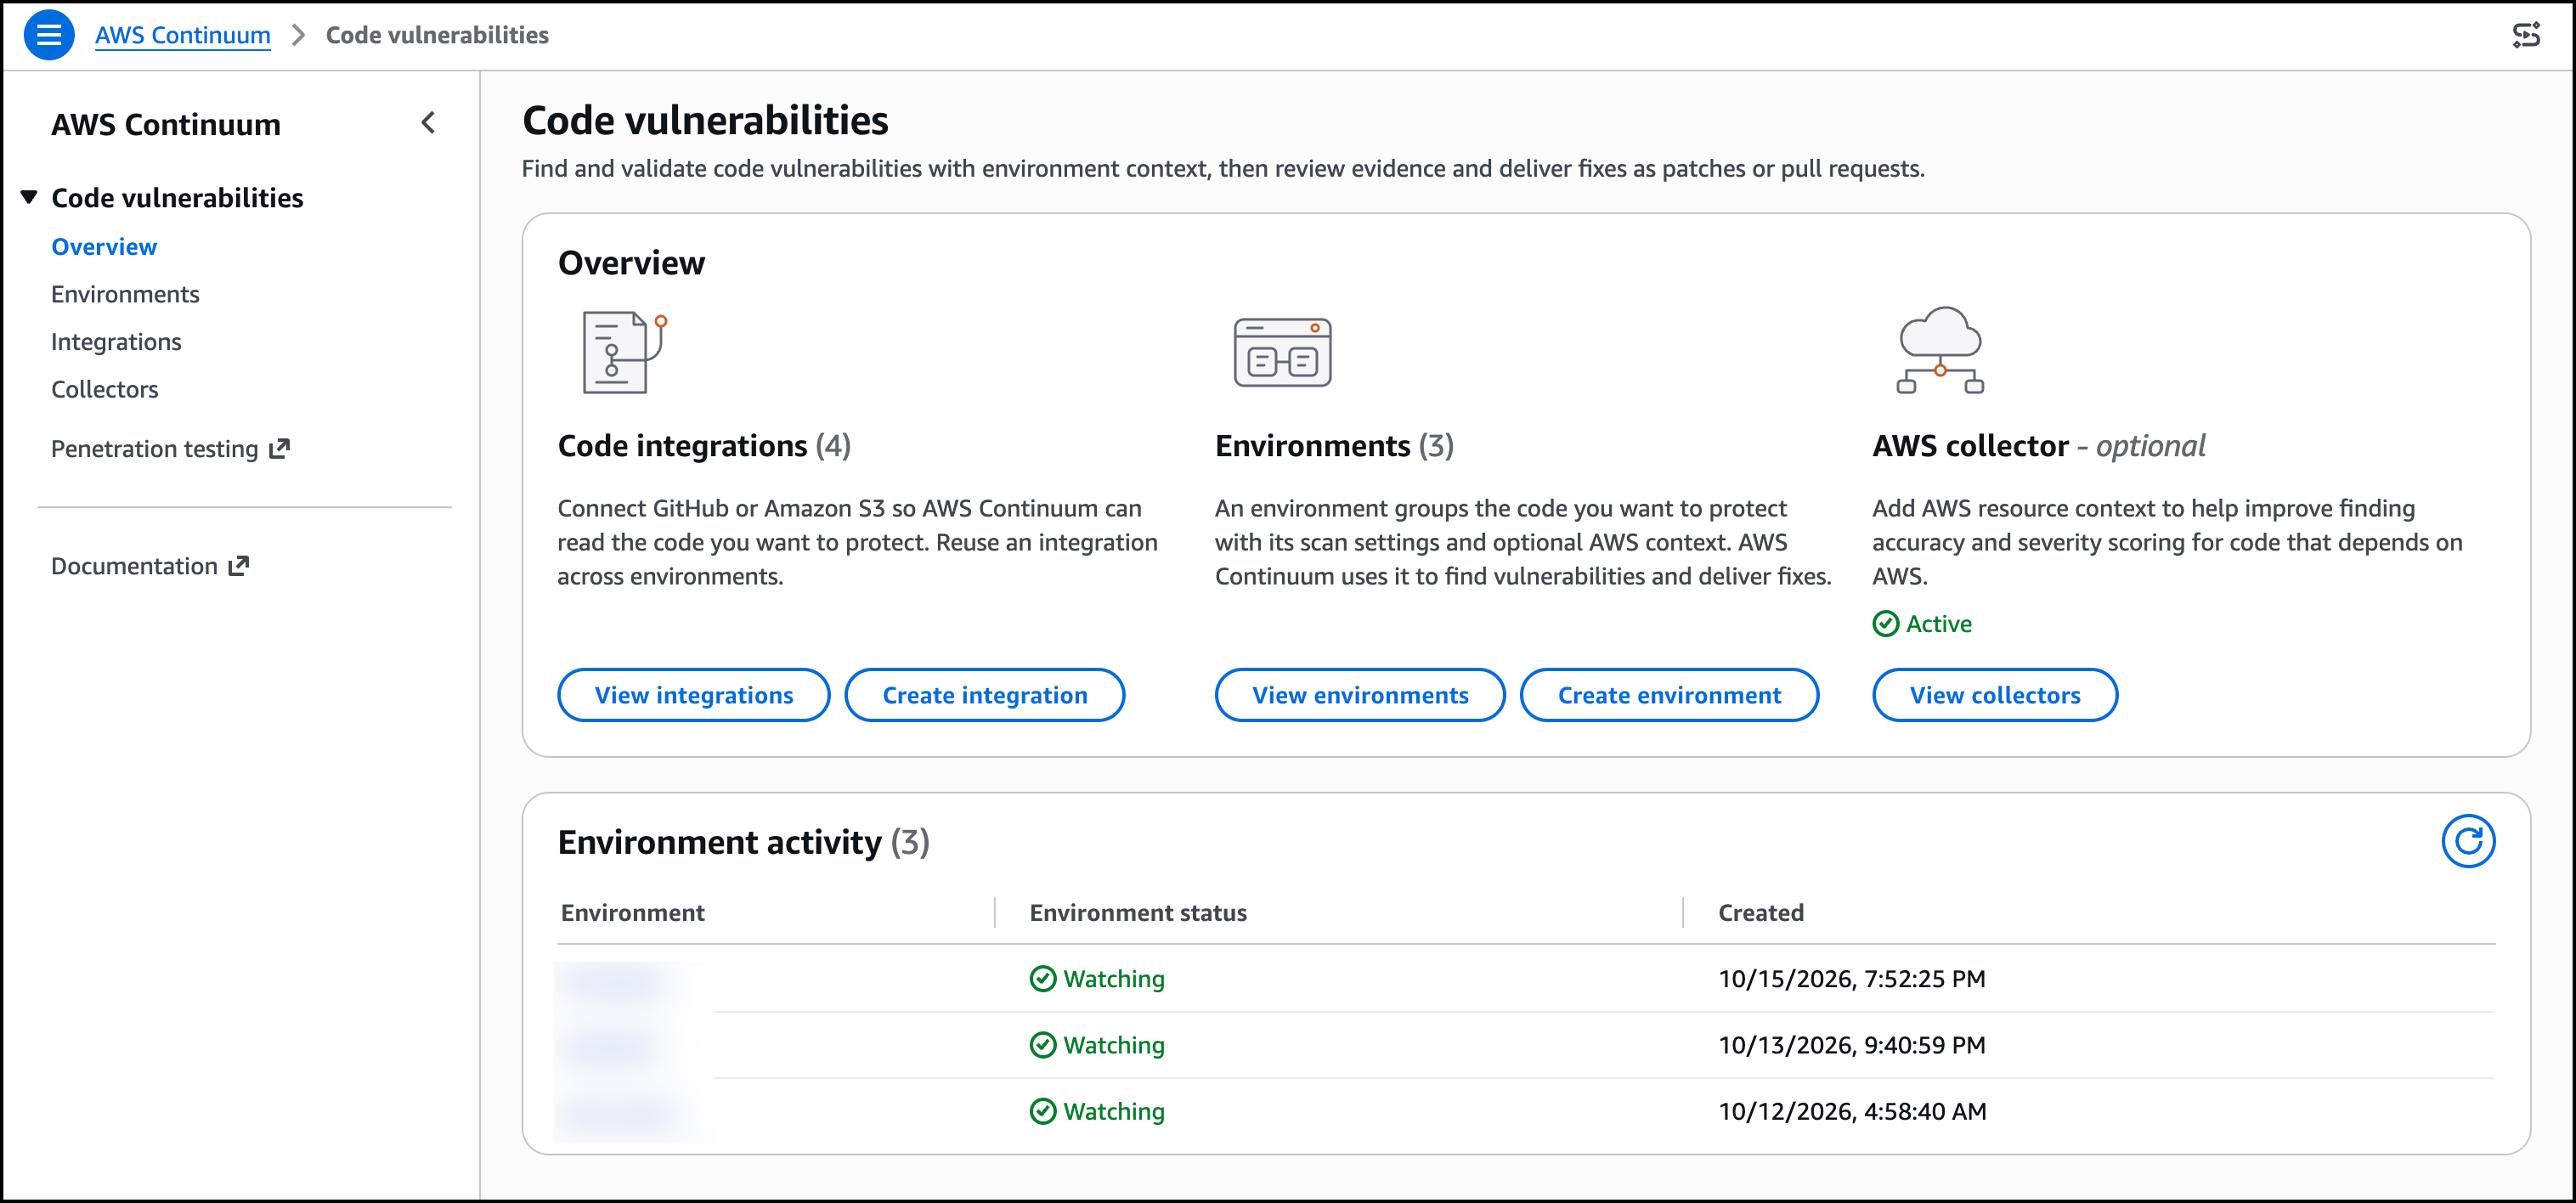
The Overview web page brings these items collectively in a single place, exhibiting my Code integrations, the Environments constructed on them, and the standing of any AWS collector that provides AWS useful resource context.
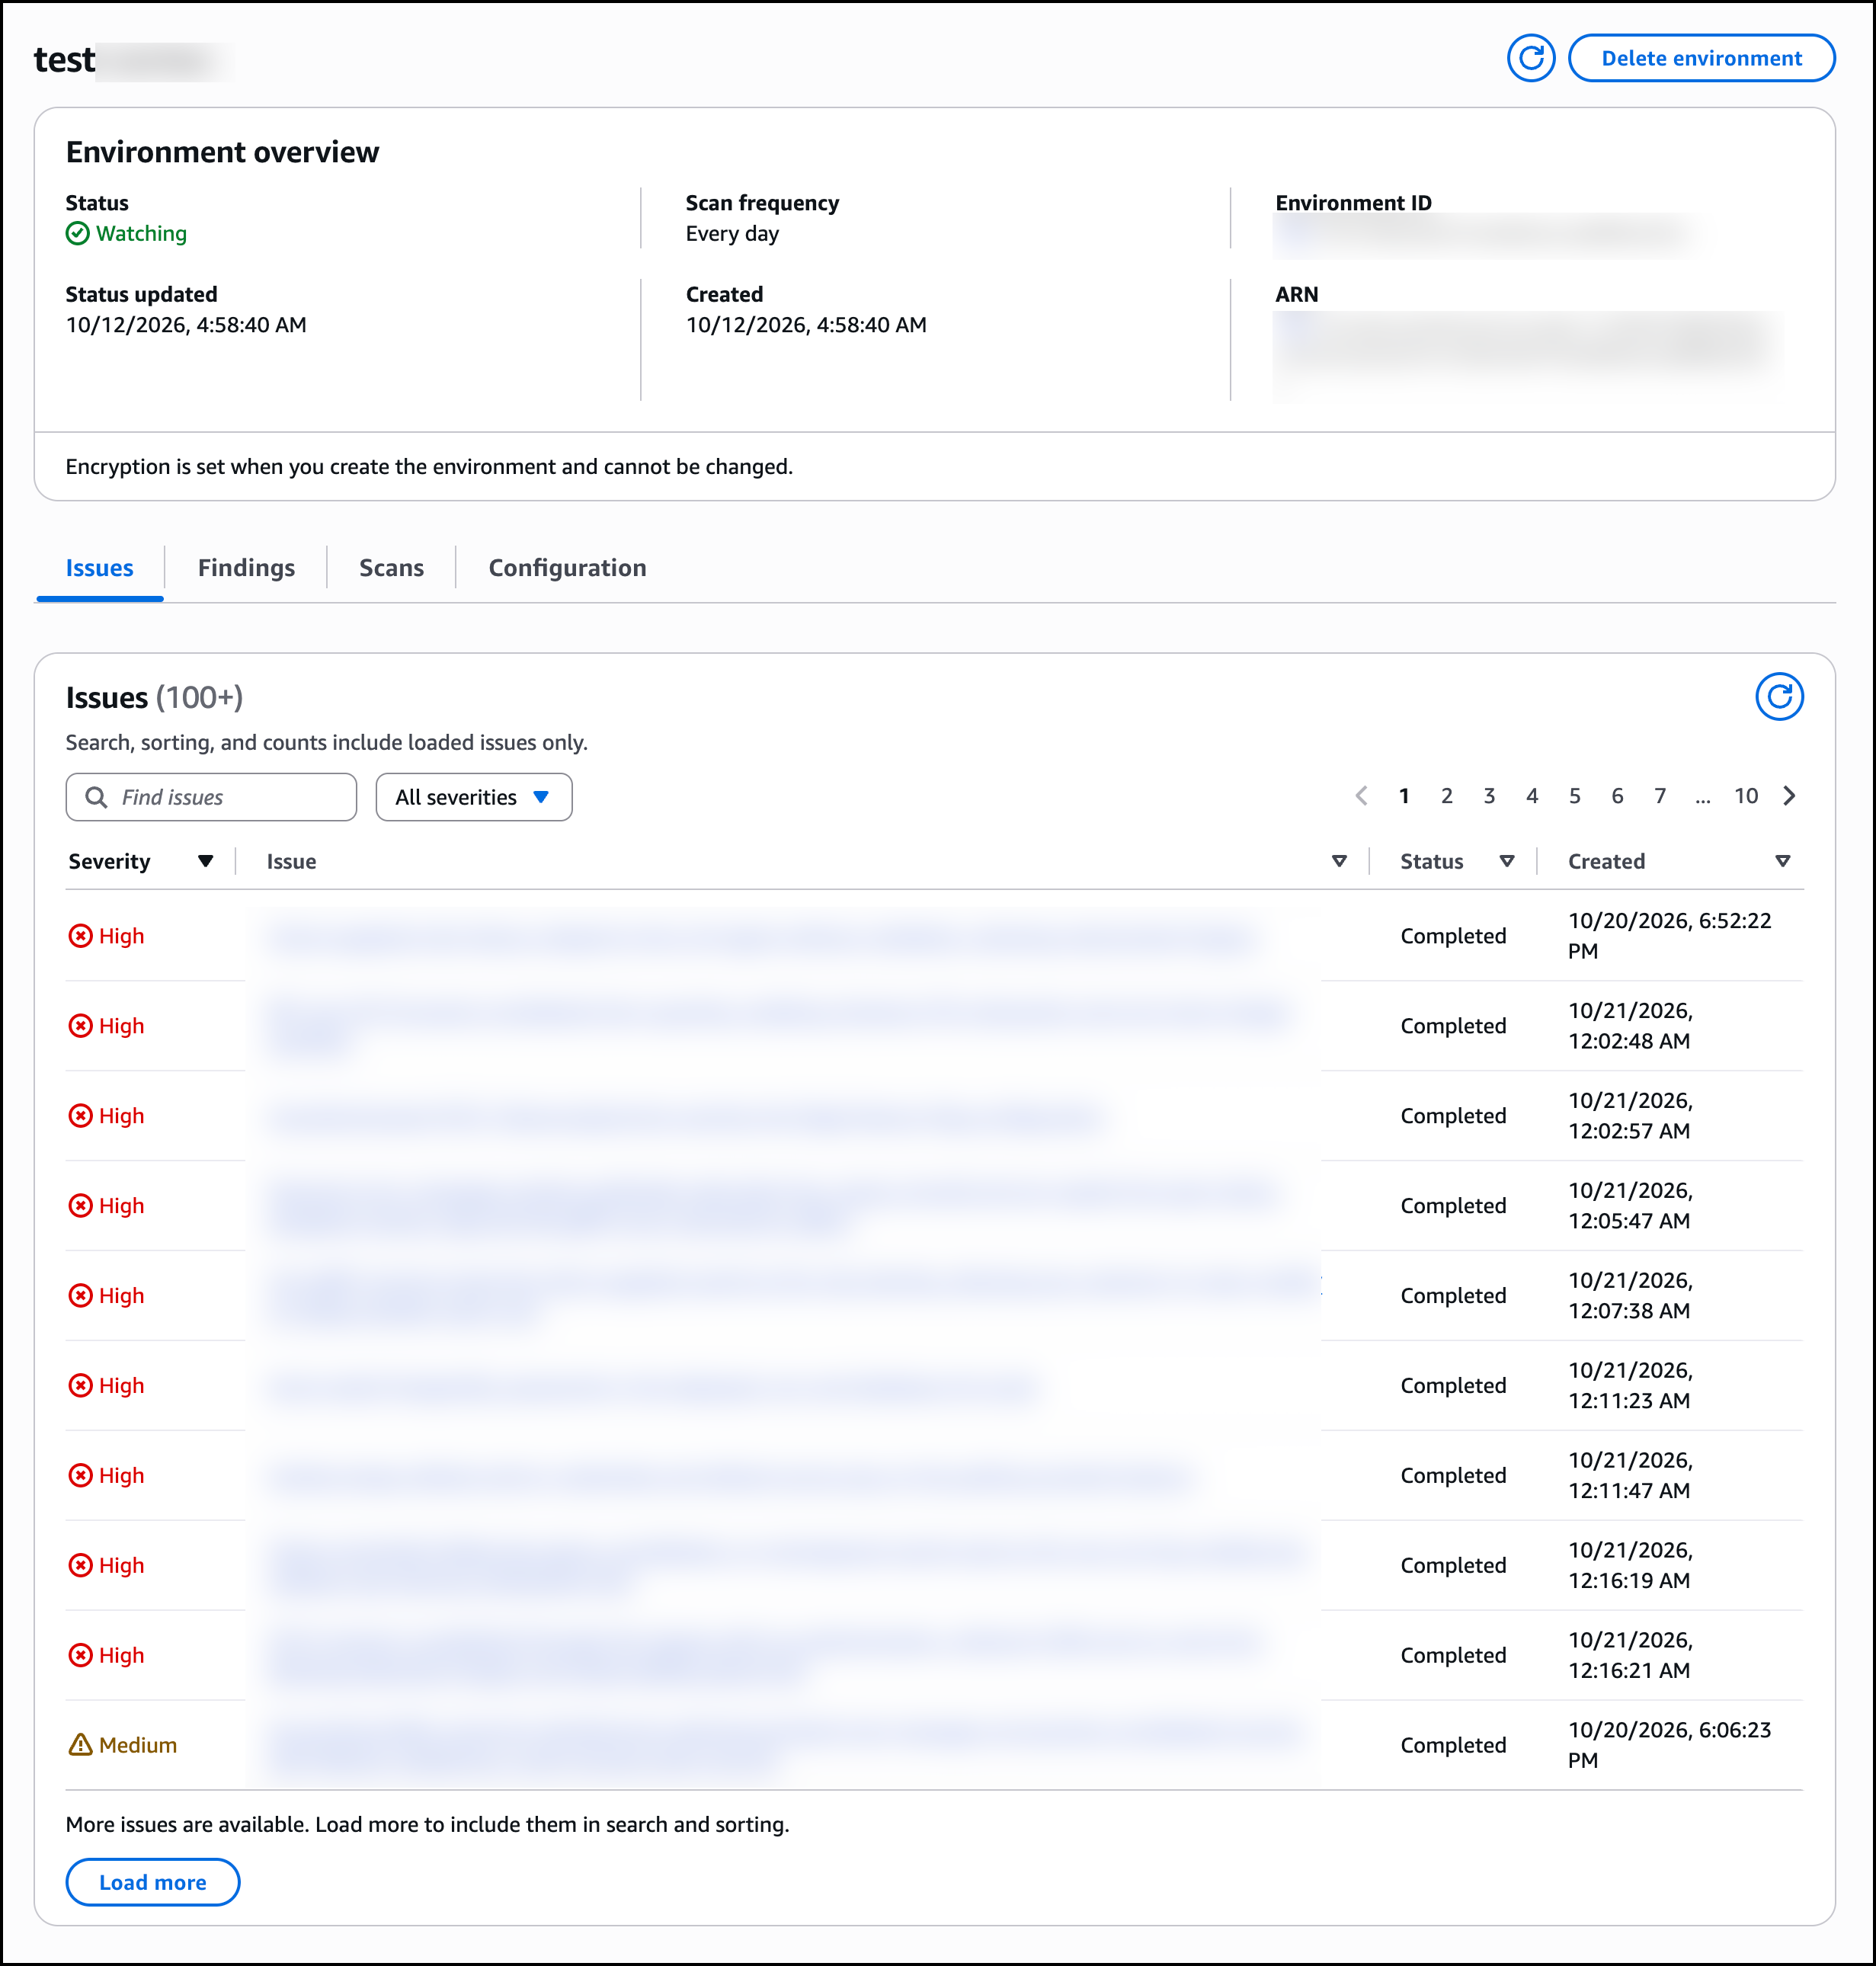
I open considered one of my environments. The Points tab lists validated, prioritized points fairly than uncooked scanner output, every with a severity, a standing, and the time it was created. I select one of many points.
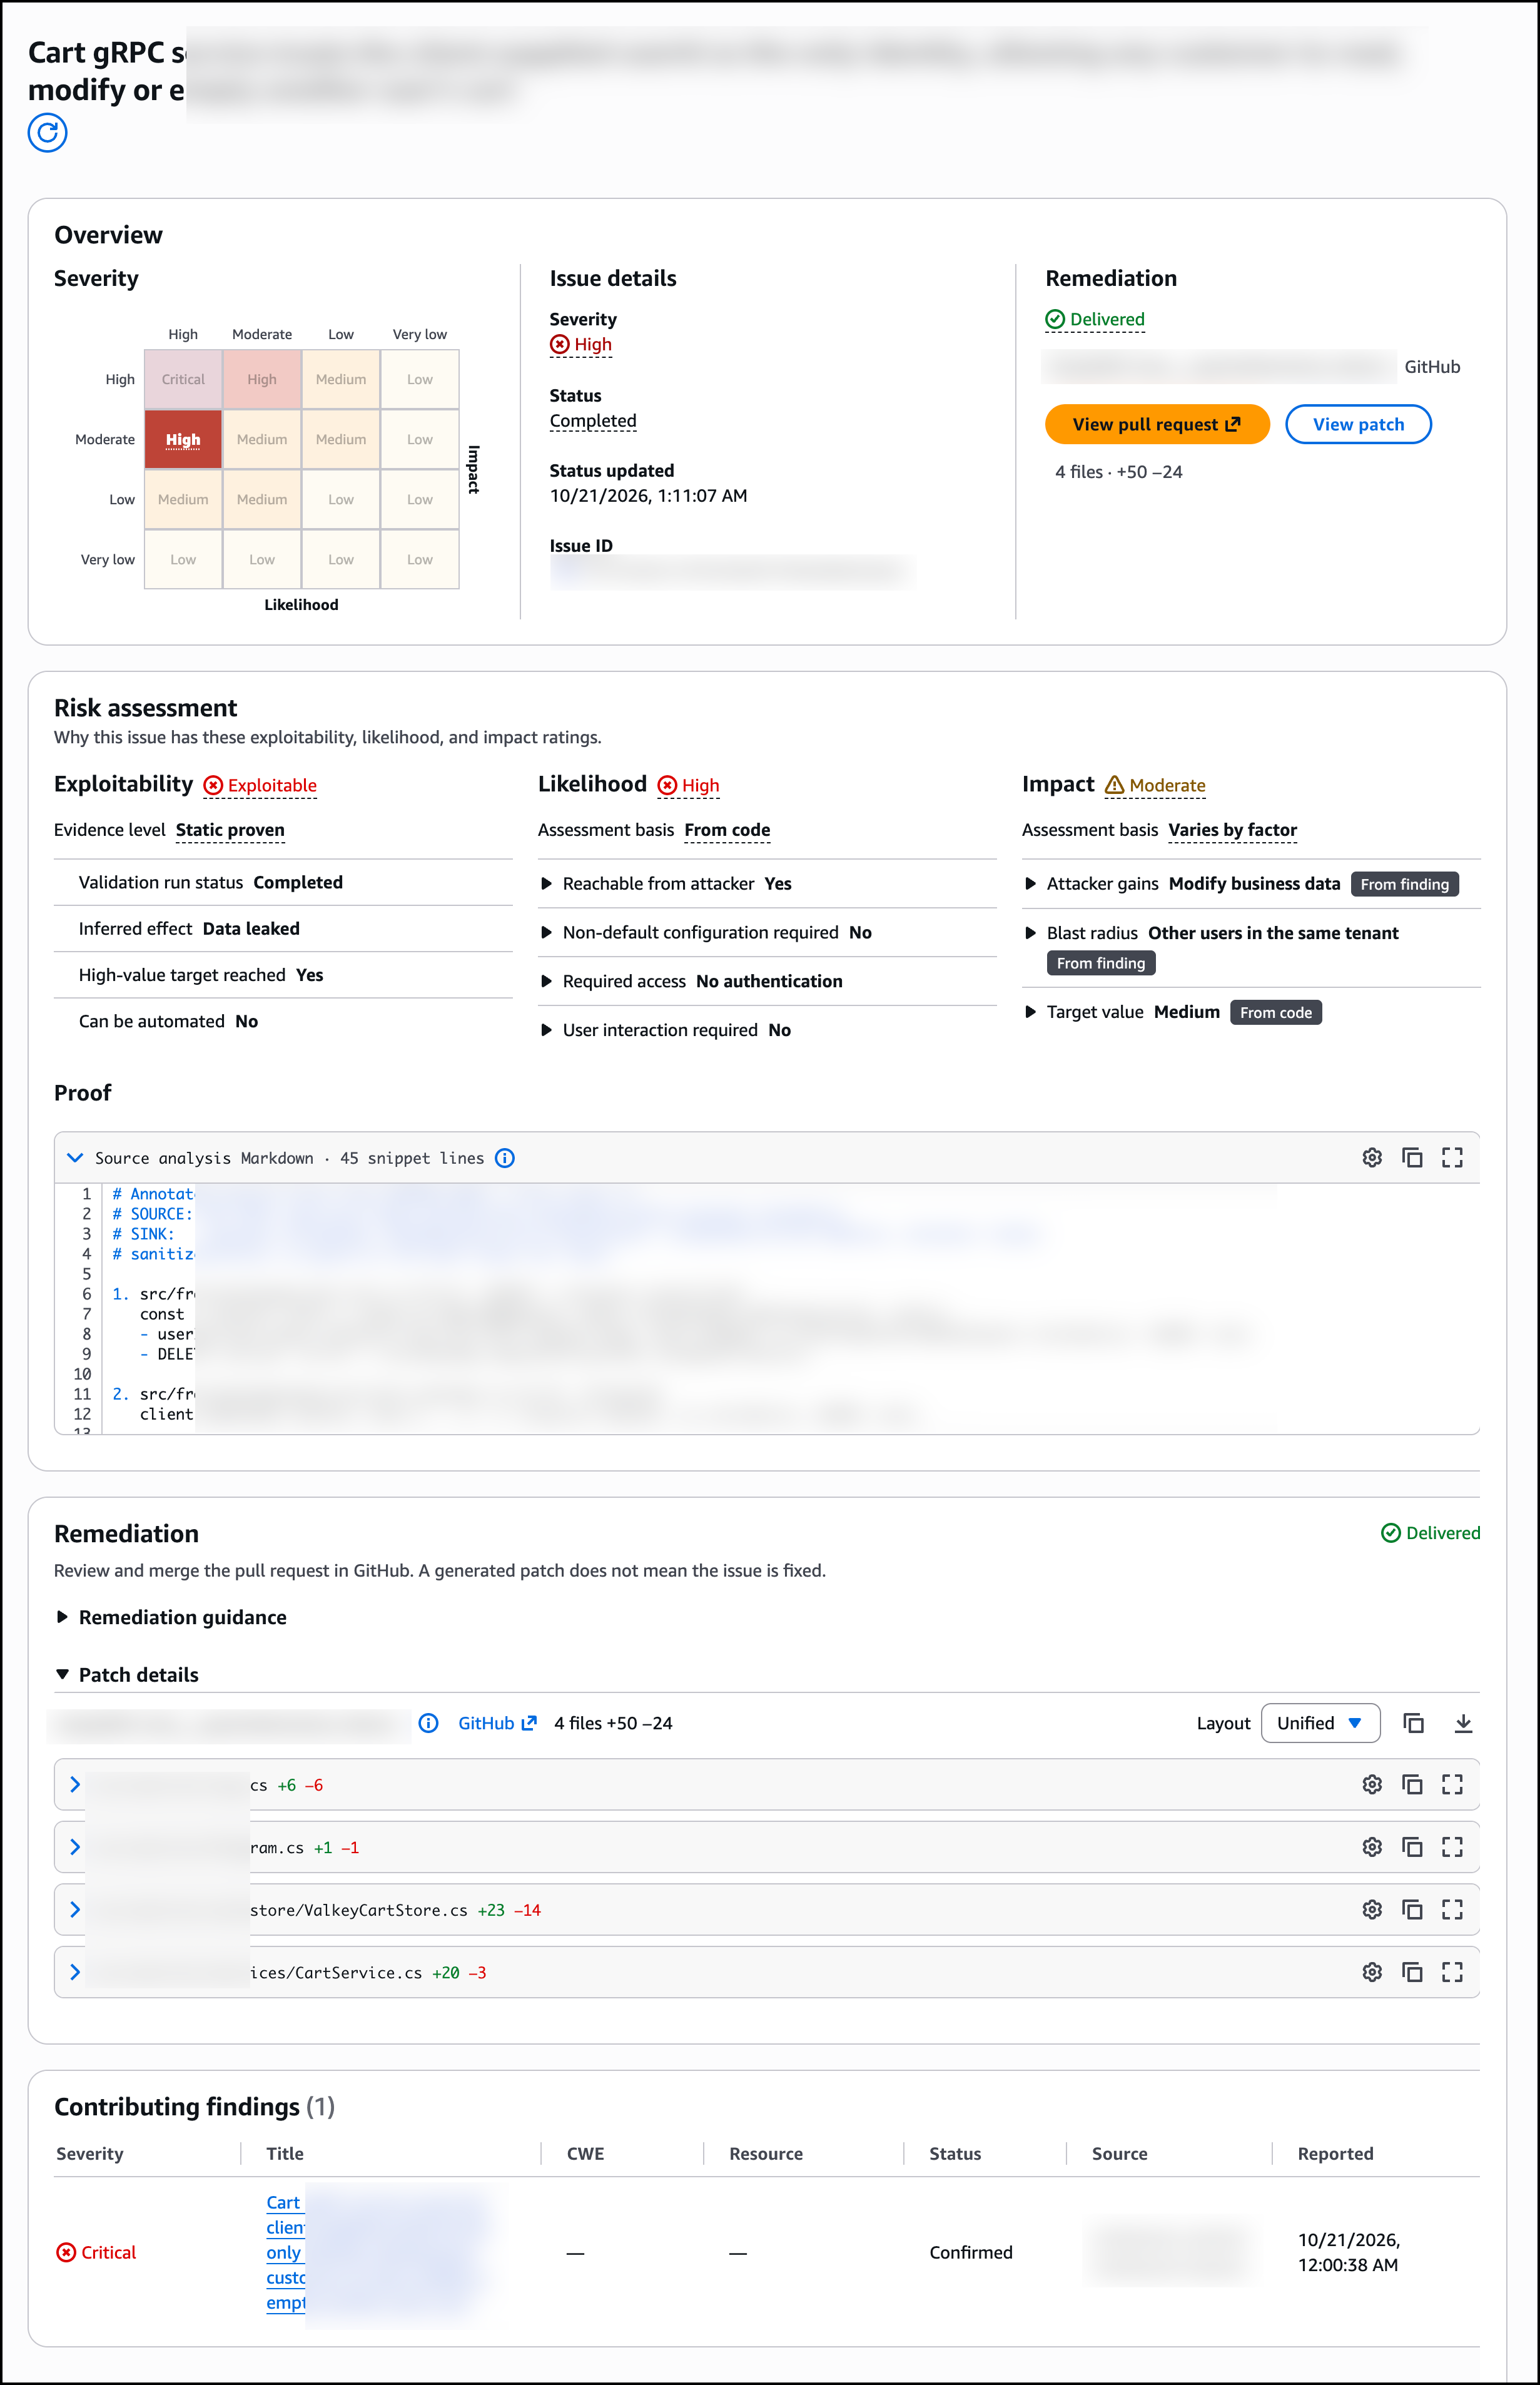
The Overview charges it Excessive severity, with the standing Accomplished and the remediation already Delivered to GitHub. The Threat evaluation explains why. Continuum charges its Exploitability as Exploitable, with an proof stage of Static confirmed and a validation run standing of Accomplished. Chance is Excessive, for the reason that service is reachable from an attacker, requires no authentication, and desires no person interplay. Impression is Reasonable, which suggests an attacker features the power to change enterprise knowledge, with a blast radius reaching different customers in the identical tenant. A Proof part contains the supply evaluation behind the decision.
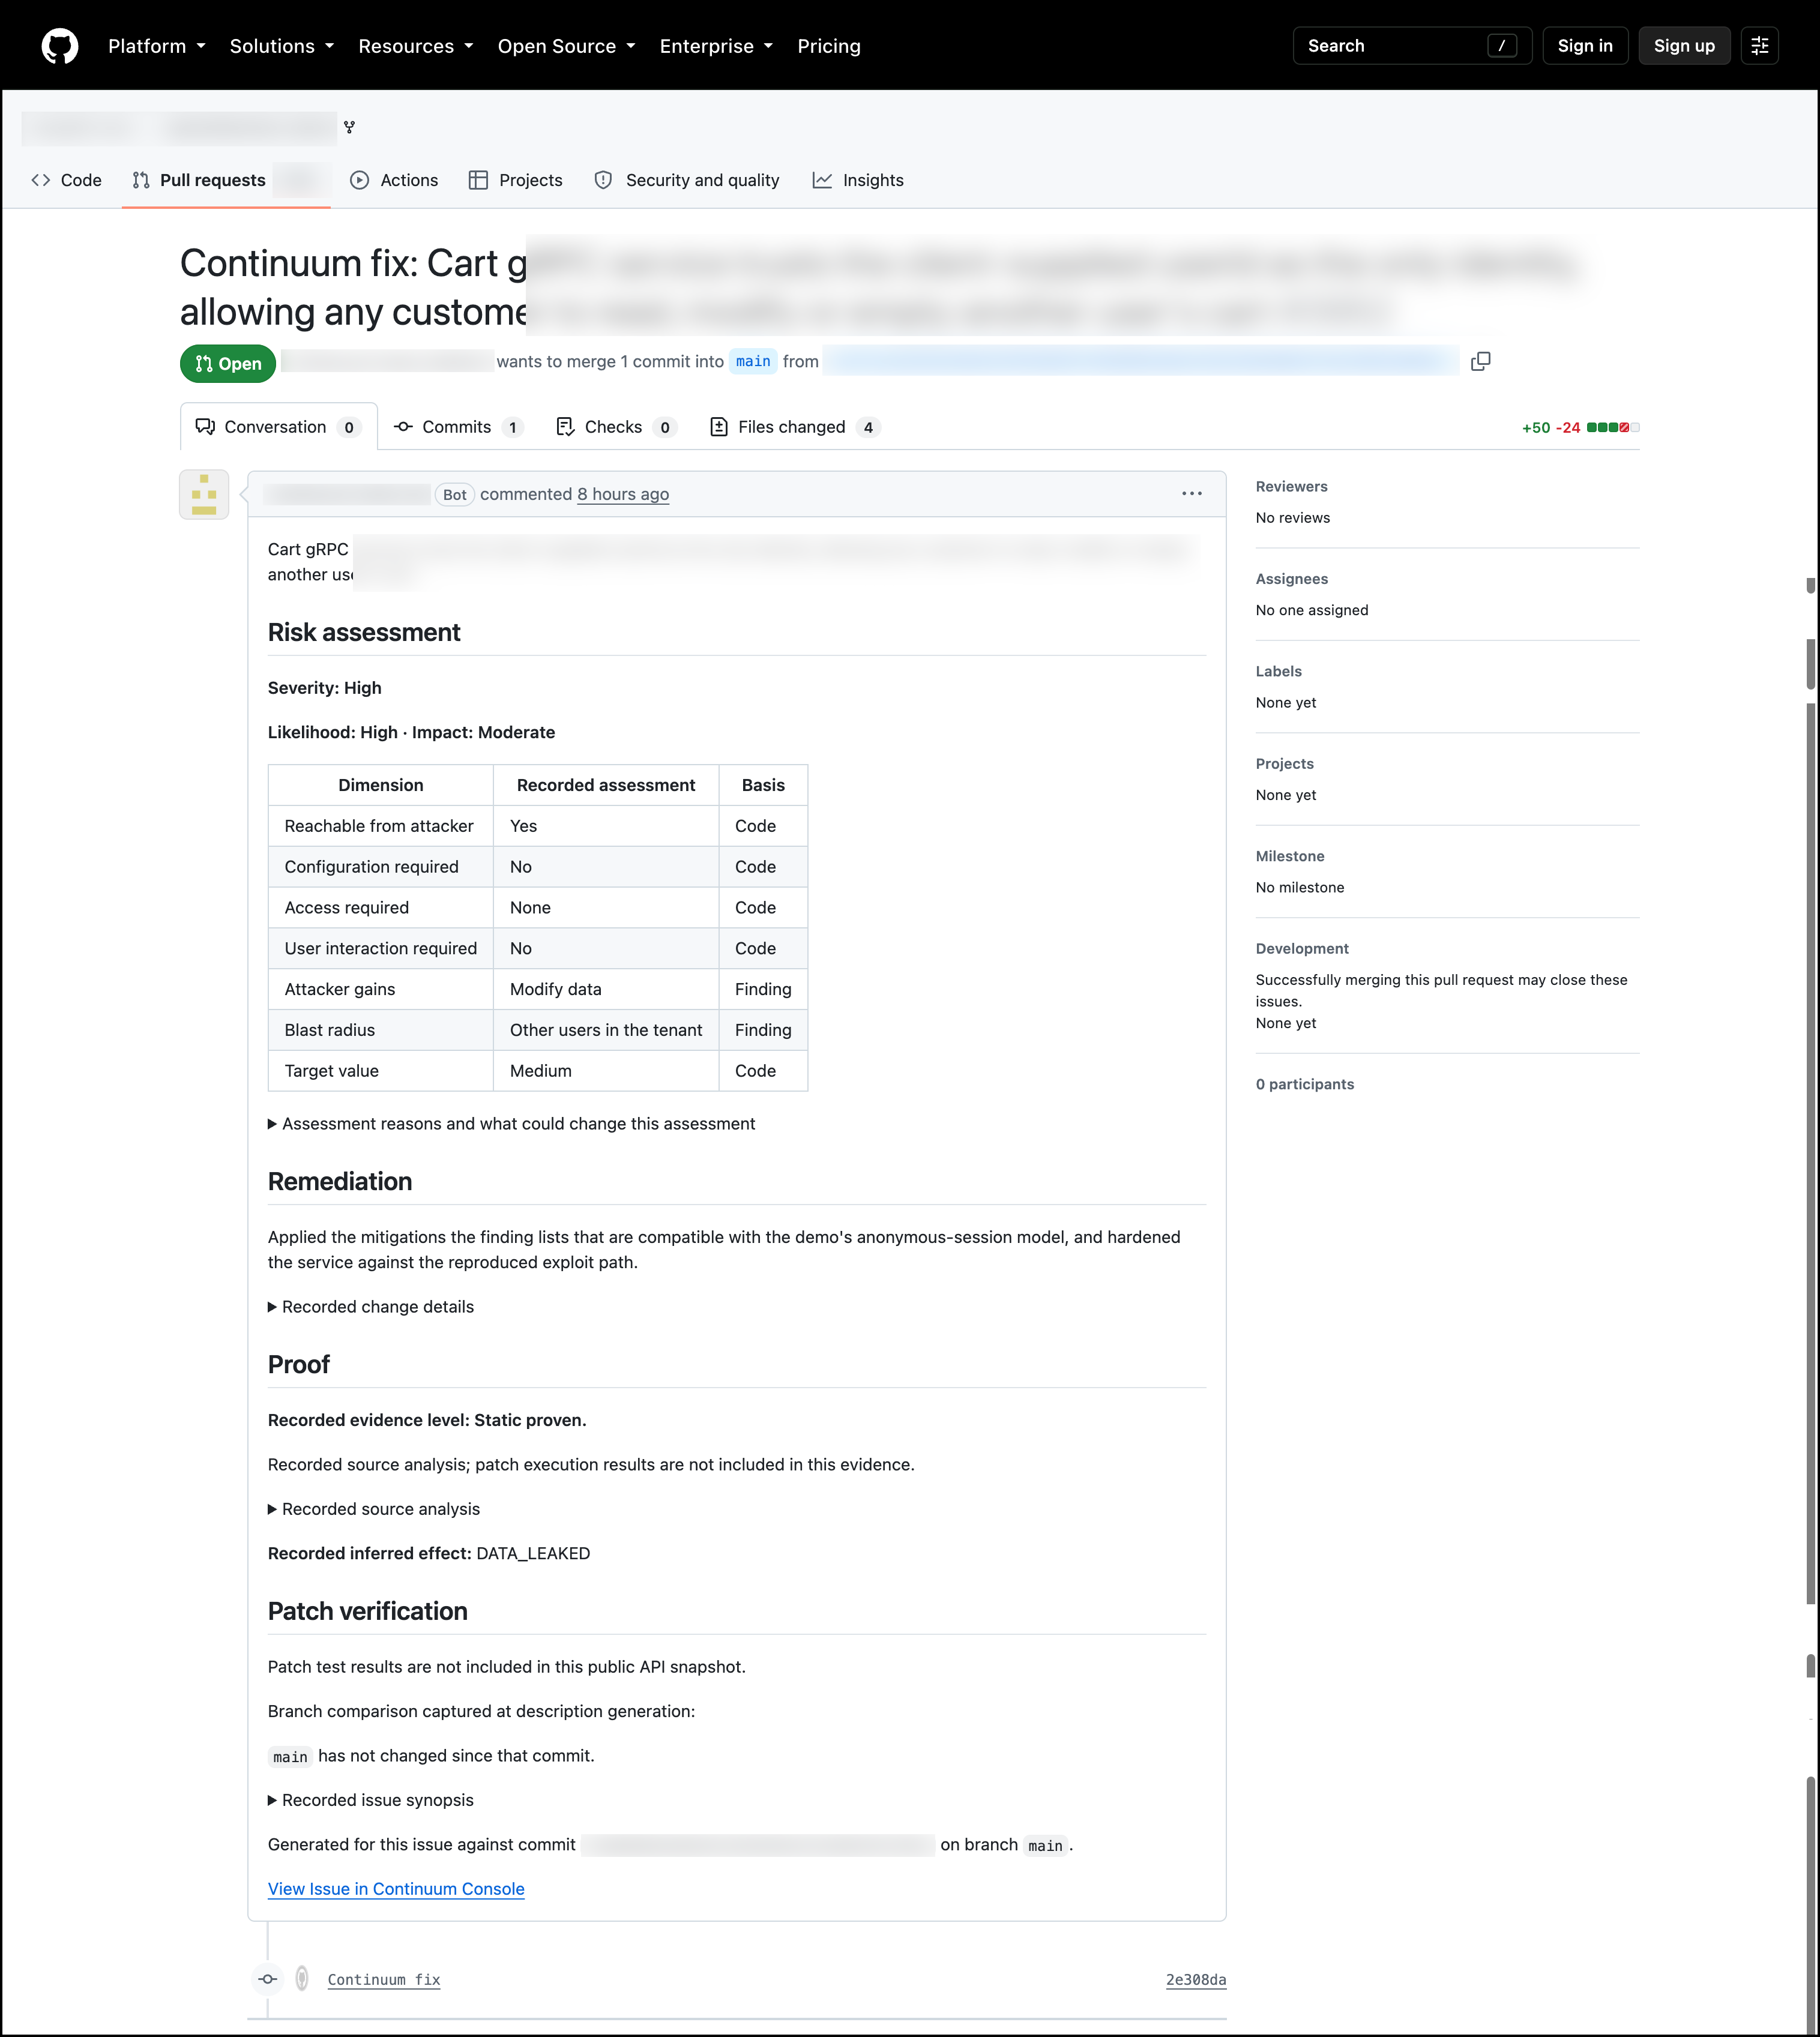
The Remediation part reveals a repair already delivered as a pull request in GitHub, altering 4 information, with 50 traces added and 24 eliminated throughout the cart service. Continuum opens the repair as a pull request titled Continuum repair, and I select View pull request to open it in GitHub. The console is express {that a} generated patch doesn’t imply the difficulty is mounted. I nonetheless evaluate and merge it, which retains the ultimate determination with my staff. A Contributing findings part lists the particular scanner discovering this difficulty was constructed from.
The pull request description carries the identical threat evaluation, remediation abstract, and proof from the console, so whoever critiques it in GitHub sees the proof with out leaving their workflow.
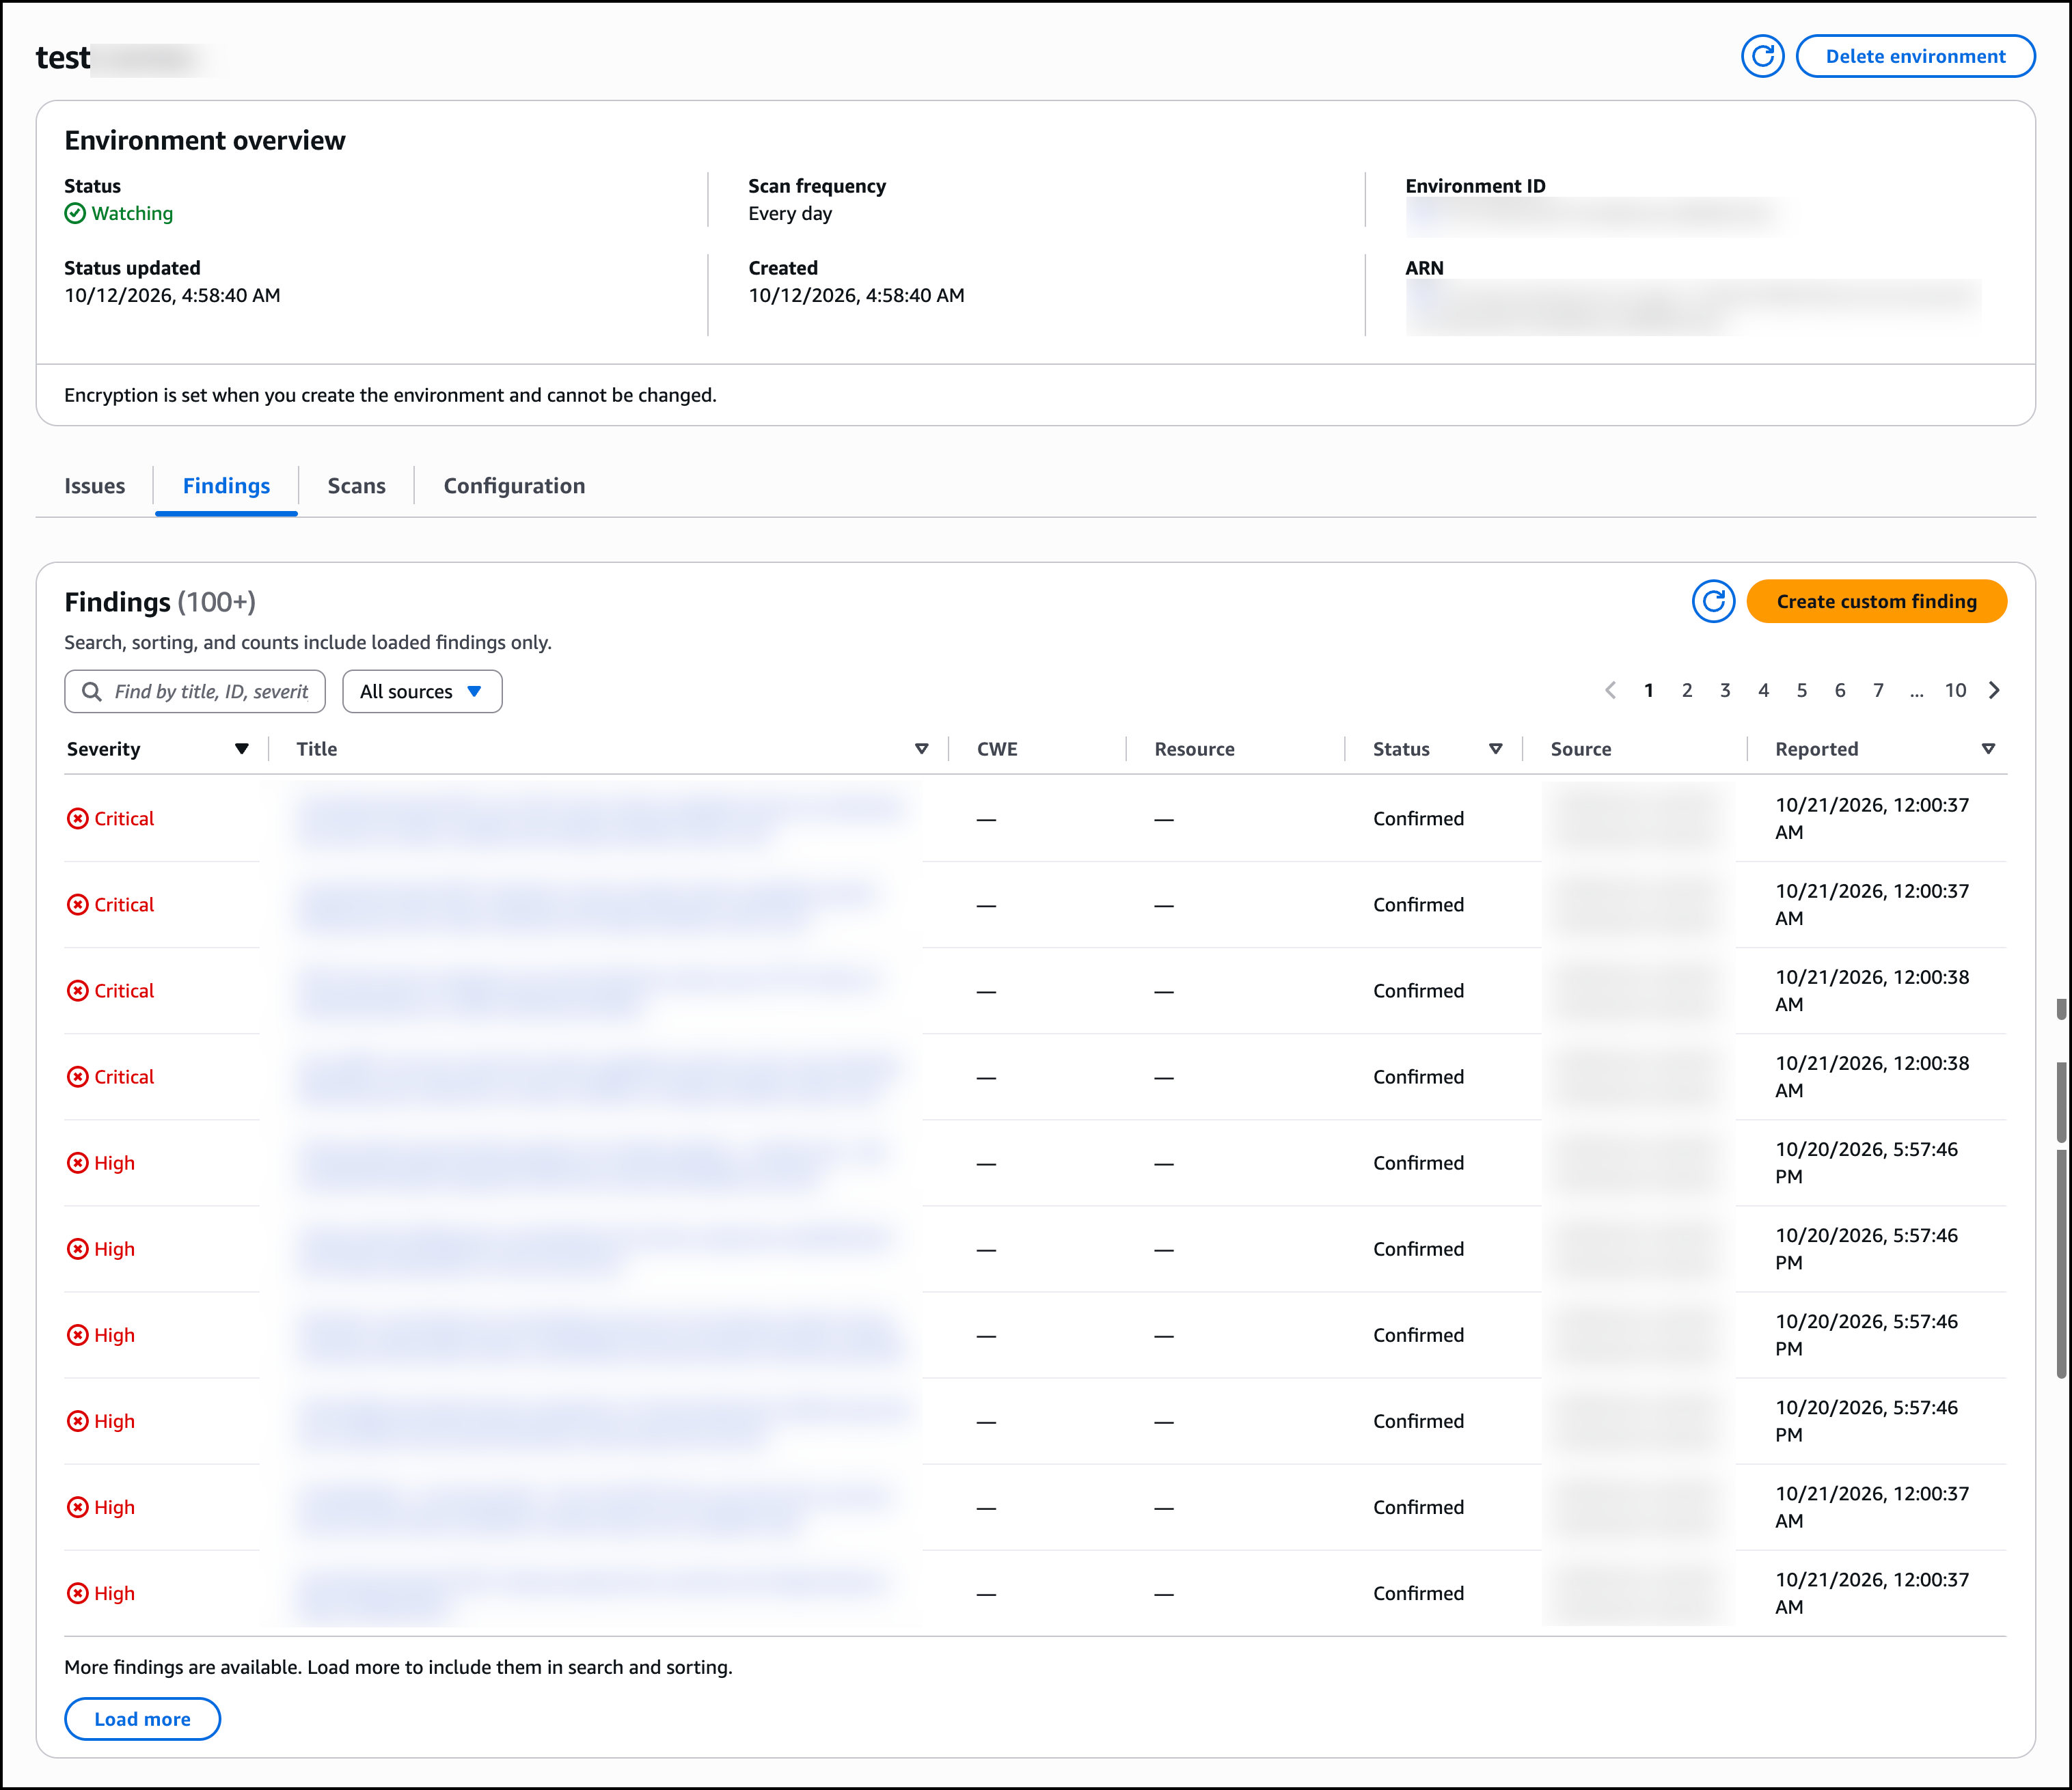
The Findings tab lists the uncooked scanner findings throughout the setting, the proof that points are constructed from.
The Scans tab reveals the historical past of every scan with its standing, origin, and request and completion instances, and I take advantage of Configure scan frequency to alter the cadence or Queue scan to run one on demand. The Configuration tab is the place I handle the setting: the code and context sources it reads from, its code integrations, setting settings reminiscent of whether or not Continuum creates remediation patches, and the AWS collectors it makes use of for AWS context.
In a single workflow, I work by way of the validated points in precedence order with every scan, reviewing the proof and scope behind every one earlier than I approve and merge the fixes I belief. Each repair waits for my approval, so the backlog retains shrinking whereas my staff retains management of what ships.
Now obtainable
AWS Continuum for code vulnerabilities is accessible in the present day in US East (N. Virginia) and US West (Oregon) Areas. For pricing, go to the pricing web page.
To be taught extra, go to the AWS Continuum for code vulnerabilities product web page and the Person Information. Give it a attempt within the AWS Continuum console in the present day, and ship us suggestions by way of your typical AWS Help contacts.